- What are PSD2, SCA, and 3DS2?
- SCA, PSD2 and 3DS2 Regulations
- What Are the Risks of SCA/PSD2 Non-Compliance?
- Exemptions for SCA and PSD2
- The Intersection of PSD2, SCA and 3DS2
- What Are the Benefits of Implementing SCA?
- How are SCA, PSD2, and 3DS2 changing?
- Akurateco’s solutions for PSD2, SCA, and 3DS2 compliance
TL;DR: PSD2 is the EU directive for payment services and stronger electronic payment security; SCA is the PSD2 requirement that verifies customers using at least two authentication factors; and 3DS2 is the online card authentication protocol that helps merchants and issuers meet SCA requirements with less checkout friction.
Since online payments have become more established in the European payment market, payment regulations must develop accordingly in order to guarantee the security of transactions. PSD2, SCA, and 3DS2 make up a trio of regulations and technologies that are determining the future of digital payments in Europe and elsewhere. Merchants, payment providers and their customers who understand how these frameworks work will find it easier to keep up as online payments change.
In this article, we’ll break down the complexities of PSD2, SCA, and 3DS2, and shed light on their significance in shaping the future of secure online payments.
What are PSD2, SCA, and 3DS2?
Several organizations shape how PSD2, SCA, and 3DS2 work in practice. The European Union established PSD2 as the legal framework for payment services, while the European Banking Authority (EBA) supports regulatory standards and guidance related to Strong Customer Authentication. EMVCo maintains the EMV 3-D Secure specification, commonly known as 3DS2, which helps card payments support secure customer authentication online.
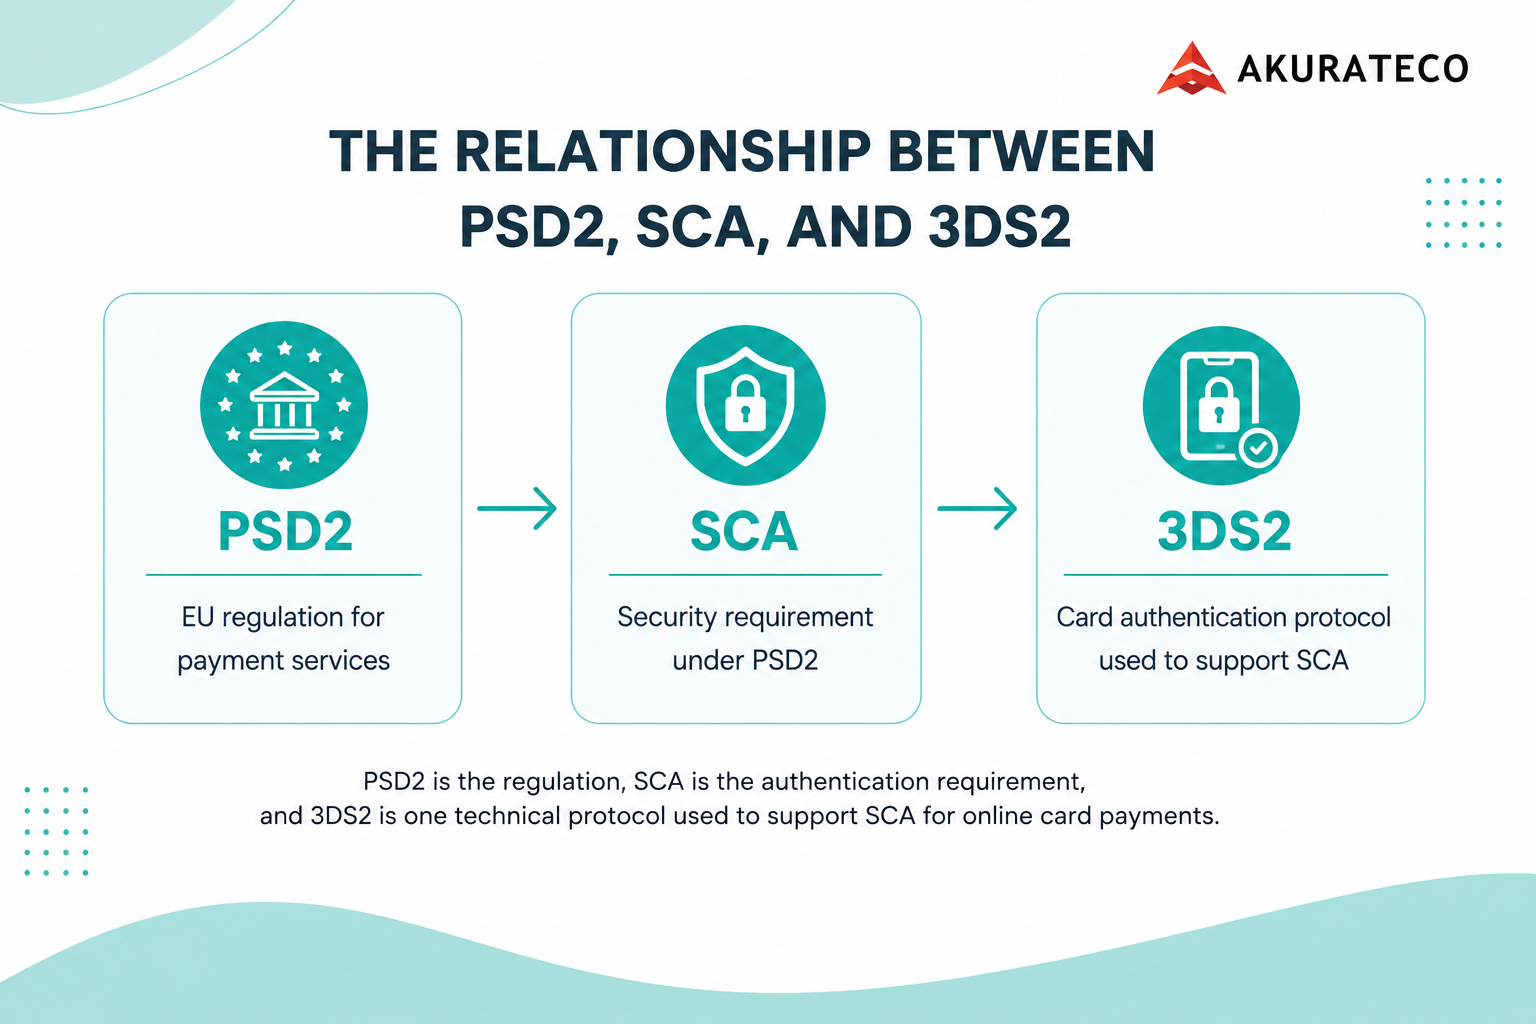
Now, let’s review each of the three in detail.
What is PSD2 (Revised Payment Services Directive)?
The second iteration of the Payment Services Directive (PSD2) is a comprehensive framework introduced by the European Union (EU) to regulate payment services and payment service providers across the EU and the European Economic Area (EEA).
PSD2 originated from the first Payment Services Directive (PSD). The first directive was initially created to build a single payment market across the European Union, making cross-border payments just as easy, efficient, and secure as domestic ones.
PSD2 introduced strict security requirements for electronic payments. It also aims to promote competition and innovation in the financial sector by allowing new companies to enter the payment market.
What is SCA (Strong Customer Authentication)?
Strong Customer Authentication (SCA) is a regulatory requirement introduced under the second Payment Services Directive. Its purpose is to increase the security of electronic payments.
PSD2 Strong Customer Authentication requires multi-factor authentication to be used in electronic payment transactions. Its objective is to greatly decrease the likelihood of fraud in online payments by verifying that the individual carrying out the transaction is actually the legitimate owner of the account. The introduction of these measures ensures that customers are protected and enhances the security of the entire digital payments system.
What is 3DS2 (3-D Secure 2.0)?
3D Secure 2 (3DS2) is the latest iteration of the 3D Secure authentication protocol, designed to secure card-not-present transactions online. It introduces a more sophisticated and user-friendly approach to authentication, leveraging advanced data exchange and risk-based assessment to minimize friction for the user during the payment process.
3DS2 leaves the method to the issuer, which can ask the cardholder to confirm in a banking app, enter a one-time code, or use biometrics. Whatever the method, the check has to combine two independent factors to count as SCA.
We explain how the 3D Secure protocol and the 3DS2 flow work step by step in a separate guide.
SCA, PSD2 and 3DS2 Regulations
Now, let’s look at the specific requirements behind PSD2, SCA, and 3DS2.
PSD2 Timeline and Milestones
- November 25, 2015: PSD2 was adopted as Directive (EU) 2015/2366, creating the revised EU framework for payment services in the internal market.
- January 13, 2018: PSD2 became applicable across the EU, bringing new rules for payment service providers, open banking access, and stronger payment security.
- September 14, 2019: The Strong Customer Authentication requirement under PSD2 started to apply, making two-factor authentication a core requirement for many electronic payments.
- December 31, 2020: The EBA set this as the final migration deadline for applying SCA to e-commerce card-based payment transactions in the EU.
- June 28, 2023: The European Commission proposed PSD3 and the Payment Services Regulation as part of a new package to modernize the PSD2 framework.
- June 10, 2025: The EBA published a no-action letter on the overlap between PSD2 and MiCA for services involving e-money tokens, an issue covered in Akurateco’s MiCA research.
- November 27, 2025: The Council of the EU and European Parliament reached a provisional political agreement on updated payment services rules, including PSD3 and the Payment Services Regulation.
- April 23, 2026: The Council of the EU published the final compromise texts of PSD3 and the Payment Services Regulation, which still need formal adoption and publication in the Official Journal.
PSD2
PSD2 introduces several key rules. One of them is the mandate for banks and financial institutions to grant access to their customers’ account data to Third-Party Providers (TPPs) upon customers’ consent. TPPs can do this through Application Programming Interfaces (APIs), which let them build financial services on top of the bank’s infrastructure. Another critical aspect of PSD2 is the enforcement of SCA.
SCA
Strong Customer Authentication regulations mandate a rigorous authentication process for electronic transactions within the European Economic Area. Specifically, SCA requires at least two independent elements from two different categories:
- Knowledge (something only the user knows, like a password or PIN);
- Possession (something only the user possesses, such as a mobile device or hardware token);
- Inherence (something the user is, including biometric features like fingerprints or facial recognition).
3DS2
3D Secure 2 is the main way online card payments meet PSD2 SCA requirements, with as few interruptions at checkout as possible. It requires merchants to send additional information with each transaction so the bank can verify the cardholder is making the purchase. If the issuer rates the payment as low-risk and can apply an SCA exemption, it goes through without a challenge. Otherwise, the cardholder is asked to confirm it.
What Are the Risks of SCA/PSD2 Non-Compliance?
Non-compliance with PSD2 and its SCA rules can result in severe consequences for financial institutions, payment service providers, and merchants. Here are some of the major risks associated with non-compliance.
- Financial penalties
National regulators, for example BaFin in Germany or the Central Bank of Ireland, can fine payment service providers that fail to meet the PSD2 SCA requirements. Member states set the amounts, but under Article 103 of PSD2 the penalties must be effective, proportionate and dissuasive. Such fines can place a heavy burden on payment service providers and have a negative impact on their financial position.
- Increased fraud liability
Non-compliance can place the liability for fraudulent transactions onto the entity that failed to implement the required SCA measures. In turn, it can lead to financial losses and compensation claims for the organization.
- Loss of consumer trust
Merchants and PSPs that do not adhere to regulatory standards are likely to be perceived as less secure, causing customers to turn to competitors.
- Operational disruptions
Delayed or insufficient PSD2 SCA compliance can cause operational disruptions, including payments that issuers decline because they arrive without SCA or a valid exemption, resulting in lost sales and revenue.
- Restricted market access
In serious cases, the national regulator can withdraw a payment institution’s authorization (PSD2, Article 13). Without it, the provider cannot offer payment services in the EU and EEA or passport them into other member states, which limits its growth opportunities.
Exemptions for SCA and PSD2
PSD2 and Strong Customer Authentication requirements include several exemptions designed to balance security with usability. They aim to reduce friction in low-risk or routine transactions, making checkout smoother for consumers while maintaining high security standards. These exemptions are set out in the regulatory technical standards on SCA, Commission Delegated Regulation (EU) 2018/389. Some notable exemptions include:
Low-value transactions
Online payments up to EUR 30 may be exempt from SCA. The exemption works only while the payer’s earlier payments since the last SCA stay within EUR 100 in total, or within five in number. The issuer decides which of the two limits it tracks.
Trusted beneficiaries
Consumers can add merchants to a list of trusted beneficiaries held by their bank, so later payments to them may skip SCA. Adding a merchant to the list requires SCA itself.
Recurring transactions
For regular payments of the same amount to the same merchant (e.g., a fixed monthly standing order), SCA is required only for the first transaction. Subsequent transactions are exempt from SCA as long as the amount and the recipient remain constant.
Charges that vary in amount, such as usage-based bills or top-ups, don’t fit this exemption. In card payments, repeat charges are usually processed as merchant-initiated transactions instead, whether the amount is fixed or not. That takes them outside SCA.
Low-risk transactions
Transactions that are deemed low-risk based on real-time risk analysis may be exempt from SCA. This assessment is conducted by the payment service provider using transaction risk analysis (TRA) tools to evaluate factors like the amount, frequency, and the user’s behavioral patterns.
The exemption has hard limits. Article 18 of the same regulation allows TRA only when three conditions are met together. The provider’s own fraud rate for that type of payment must be at or below the reference rate in the Annex, and the amount must not exceed the threshold that the Annex pairs with that rate. The real-time risk analysis also must not flag anything unusual, such as an abnormal payer location or a known fraud scenario.
| Transaction amount | Reference fraud rate, remote card payments | Reference fraud rate, remote credit transfers |
|---|---|---|
| Up to EUR 100 | 0.13% | 0.015% |
| Up to EUR 250 | 0.06% | 0.01% |
| Up to EUR 500 | 0.01% | 0.005% |
The fraud rate is the value of fraudulent payments divided by the value of all remote payments of the same type, counted over a rolling 90-day period. Payments made with SCA and under exemptions both count. Either the issuer or the acquirer can apply TRA, each based on its own fraud rate, so the limit a merchant gets depends on whose rate counts. For card payments, the issuer still has the final say and can require SCA or decline the payment. If a provider’s rate stays above the reference rate for two consecutive quarters, it has to stop using the exemption in that band.
Outside the scope of SCA
Some payments need no exemption because SCA doesn’t cover them at all. The main group is merchant-initiated transactions. The customer authenticates once, when agreeing to future charges. There is a separate guide on how merchant-initiated transactions are treated under SCA. Mail and telephone orders (MOTO) are also out of scope, since the payer doesn’t start them online. One-leg-out payments, where the issuer or acquirer sits outside the EEA, are only partly covered. The EBA expects SCA there on a best-effort basis.
Secure corporate payments made through dedicated business processes, which the national regulator accepts as equally safe, have their own exemption.
The Intersection of PSD2, SCA and 3DS2
In short, PSD2, SCA, and 3DS2 are connected but not interchangeable. PSD2 is the directive, SCA is the authentication requirement introduced under that regulatory framework, and 3DS2 is one of the main card-payment protocols used to help merchants and issuers authenticate online transactions in a PSD2/SCA-compliant way.
The combination of PSD2, SCA, and 3DS2 marks a pivotal shift towards a more secure and user-centric digital payment environment. PSD2 acts as the legislative backbone, promoting open banking and mandating the adoption of SCA to ensure electronic payments are executed with robust security measures.
In turn, SCA, as a core component of PSD2, introduces a critical layer of security by requiring multi-factor authentication for online transactions. However, the complexity of implementing SCA could add friction to transactions and discourage consumers from online purchases.
This is where 3DS2 comes in. It is the technology that reconciles the requirements of PSD2 and SCA with the need for a low-friction payment experience. It addresses the challenges posed by its predecessor (3DS1) by facilitating a smoother transaction process, capable of transmitting extensive data to assess transaction risk in real time.
What Are the Benefits of Implementing SCA?
Strong Customer Authentication offers several significant benefits, central to enhancing security and trust in the digital payment landscape. Among them are:
- Reduced fraud rate
By requiring multi-factor authentication, SCA makes it much harder for fraudsters to take over and use payment accounts.
- Increased customer trust
Knowing that transactions are protected by robust security measures, clients are more likely to make purchases on a merchant’s website or application.
- Regulatory compliance
Applying SCA where it’s required is part of how payment service providers meet PSD2 in the EEA. Merchants take part by passing the data their acquirer needs for authentication.
- Commitment to innovation
SCA implementation drives authentication technology innovation, leading to the development of secure, efficient, and user-friendly verification methods.
How are SCA, PSD2, and 3DS2 changing?
While PSD2, SCA, and 3DS2 have established a solid regulatory foundation, they continue to evolve in response to technological advances, emerging threats, and changing consumer behaviors.
Strong Customer Authentication requirements are evolving to make wider use of newer authentication methods, such as biometrics and behavioral analytics.
The biggest PSD2 changes are coming with PSD3 and the Payment Services Regulation (PSR). The European Commission proposed the package in June 2023. The Council of the EU and the European Parliament reached a provisional agreement on November 27, 2025, and the Council published the final compromise texts on April 23, 2026. As of October 2026, both texts still await formal adoption and publication in the Official Journal of the EU.
The package splits PSD2 in two. PSD3 remains a directive and covers licensing and supervision. The PSR is a regulation that applies directly in every member state, and the SCA rules move into it. The PSR enters into force 20 days after publication in the Official Journal and applies about 21 months later, which in practice means 2028.
These two changes touch authentication and fraud liability:
- SCA has to work for everyone. Providers must offer at least one way to authenticate that doesn’t depend on owning a smartphone and suits older customers, people with disabilities and those with low digital skills.
- Impersonation fraud gets its own refund right. If a fraudster poses as the customer’s payment provider, for example by spoofing its phone number, email, website or app, and the customer authorizes a payment as a result, the provider must refund it in full. The customer has to report the fraud to the provider and to the police without undue delay. The burden is on the provider to show that the customer acted fraudulently or with gross negligence.
3D Secure 2 is also being enhanced to improve its risk-based authentication model. Visa and Mastercard ended support for EMV 3DS 2.1 in September 2024 and made 2.2 the minimum, while several schemes have been adding 2.3.1 since. By doing so, the 3DS2 protocol aims to become more adept at identifying genuine transactions and reducing false declines. Enhancements are also focused on greater integration with mobile payment systems, acknowledging the shift towards mobile-first consumer behaviors.
Akurateco’s solutions for PSD2, SCA, and 3DS2 compliance
For PSPs and acquiring banks, much of the work behind PSD2, SCA and 3DS2 is engineering. The issuer needs complete authentication data, acquirers expect exemption requests in their own formats, and a missing flag can end in a decline.
Akurateco is a white-label payment gateway and payment orchestration platform. It does not process transactions itself: clients bring their own acquiring, and the platform supplies the technical side of authentication. Akurateco’s infrastructure is PCI DSS v4.0.1 Level 1.
The platform collects the data 3DS2 needs and orchestrates the 3DS flow, whether authentication runs on the acquirer’s side or through an external MPI. With an external MPI, the PSP sets low-value and TRA exemption requests or a challenge preference in its routing rules. On selected connectors, merchants can pass exemption requests themselves. Merchant-initiated and MOTO payments are flagged as such, and each payment is routed by its authentication result.
The licensed PSP or acquirer still owns SCA compliance, decides which exemptions to request, and carries the fraud liability attached to them. The platform is deployed for licensed PSPs and banks under SAMA, QCB and FRA supervision. PSPs also get 700+ integrations and built-in tools such as intelligent routing, cascading, tokenization, and smart invoicing.
FAQ
What does PSD2 stand for?
PSD2 stands for the Revised Payment Services Directive, also called the second Payment Services Directive. It is Directive (EU) 2015/2366, adopted on November 25, 2015, and applicable since January 13, 2018. PSD2 regulates payment services and payment providers across the EU and EEA. It opened account access to third-party providers and introduced Strong Customer Authentication.
What are the SCA requirements?
SCA requires at least two independent elements from two different categories. The three categories are knowledge (a password or PIN), possession (a phone or hardware token) and inherence (a fingerprint or face scan). It applies when a customer pays electronically or accesses an account online in the EEA. Some payments qualify for exemptions, such as low-value or low-risk transactions, and some fall outside SCA altogether.
What does SCA authentication mean?
SCA authentication means Strong Customer Authentication, the check a payment provider runs to confirm that the person paying is the real account or cardholder. Under PSD2, it has to combine at least two independent factors, such as a banking app confirmation plus a fingerprint. For online card payments, the check usually runs through 3DS2, and the issuer decides which method to use.
What is the difference between PSD2 and 3DS2?
PSD2 is an EU directive, while 3DS2 is a technical protocol maintained by EMVCo. PSD2 sets the rules, including Strong Customer Authentication, but doesn’t require 3DS2 by name. In practice, 3DS2 is the main way online card payments meet SCA. It sends transaction data to the issuer, which either skips the challenge when an exemption applies or asks the cardholder to confirm.