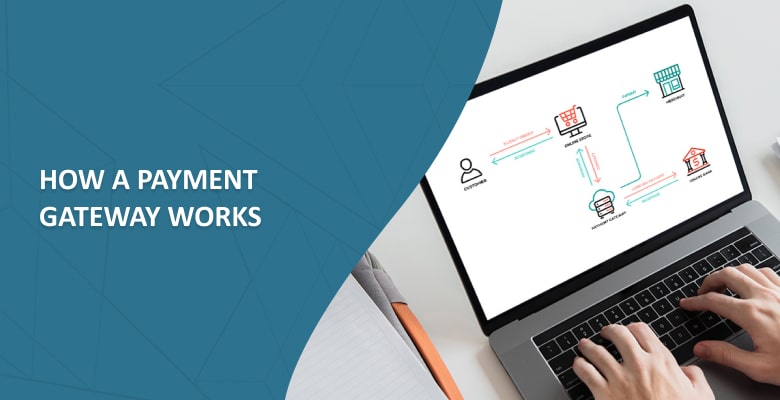
A payment gateway is the software that collects a customer’s payment details at checkout, protects them, and sends them to the merchant’s acquiring bank. Then the gateway lets the checkout know whether the payment was approved or declined. From the customer’s side, it all takes a few seconds. During this short period, a payment gateway does a lot of work to move the transaction safely.
This article explains what a payment gateway does, how merchants connect to one, how it differs from a payment processor, and how it protects card data.
What is a payment gateway?
A payment gateway is the technology that connects a merchant’s online checkout to the acquiring bank, so the merchant can accept payments on a website or in an app. Merchants usually get a gateway from a payment service provider (PSP) or from their acquiring bank.
In online transactions, a payment gateway is the online equivalent of a Point of Sale (POS) terminal or card reader used in card-present transactions. In a shop, the terminal reads the card and sends the details on for approval. Online, there is no terminal. The customer types the details into a checkout form, and the gateway takes over the terminal’s job.
Many gateways handle more than cards. Digital wallets and bank payments often run through the same gateway, so the merchant connects once and can offer several ways to pay.
What does a payment gateway do?
A payment gateway takes in the customer’s payment details, keeps them safe, and brings back an answer from the bank. All this happens in the few seconds between the customer clicking Pay and seeing the result. Later, the gateway also supports charging an approved payment and issuing a refund.
Here are payment gateway functions:
- Collects the customer’s payment details on a checkout page, in an app, or through a payment link.
- Encrypts the details and swaps the card number for a token, a stand-in value that is useless outside the gateway.
- Screens the payment for fraud and starts 3D Secure, an extra check where the customer’s bank may ask them to confirm the payment.
- Routes the payment request to the acquiring bank or its processor.
- Returns the result to the checkout, so the customer knows at once whether the payment was approved or declined.
- Handles what comes after, such as capturing approved payments and sending refunds.
Behind each of these jobs sits its own piece of software. Our guide explains how gateway software is built, layer by layer.
Capture often confuses people new to payments. An approved payment is first only reserved on the customer’s card, and capturing it turns that hold into a real charge. Some merchants capture at once, others when the order ships.
The payment gateway process ends at checkout, while the money itself moves later. We walk through the full payment processing flow, from checkout to settlement in a separate article.
Payment gateway integration methods
There are four classic ways to connect a website to a payment gateway. They range from a hosted payment gateway that sends the customer to a separate page to an integration the merchant builds and runs on its own side. A difference between the methods of integration lies in the way sensitive information is stored and transmitted. The more control a merchant wants over the checkout, the more of the security work it takes on.
Hosted Gateway
A hosted payment page is located outside the merchant’s website. You have probably seen this type of gateway integration when a website redirected you to a separate page to pay for a product or service. The main feature of this method is that the customer’s sensitive data is processed on the gateway’s payment page without passing through the merchant’s website. The advantage is that the merchant does not handle sensitive payment data directly, which can reduce their PCI DSS compliance scope and security responsibilities. However, the disadvantage is that the customer may lose confidence in the merchant the moment they are redirected to another website and leave without completing the purchase.
Server Integration
Unlike a hosted gateway, the server integration method (SIM) initiates a transaction directly on the merchant’s website. The merchant’s server prepares the payment request, and the payment gateway servers take over the processing from there. One of SIM’s main benefits is that the merchant can customize the gateway’s payment page to match its brand. The customer still completes the payment on that page, but it looks like part of the merchant’s store, and the merchant never handles the card details.
Direct Post
Direct Post keeps the payment form on the merchant’s own website. The difference is that the card details go from the customer’s browser straight to the payment gateway and never reach the merchant’s servers. Since the merchant does not receive or store the customer’s sensitive information, Direct Post can reduce the merchant’s PCI DSS scope, though less than a hosted page does. The downside is that the form sits on the merchant’s page, so the merchant has to keep that page secure. If attackers tamper with it, they can steal card details as the customer types them.
Advanced Integration Method
Advanced integration method (AIM) is for merchants who want to fully manage their customers’ online payment experience. With AIM, the customer pays on the merchant’s own payment form, so the site needs a TLS (SSL) certificate to protect the card details on their way in. The merchant’s server then sends each transaction to the gateway over an encrypted connection. This option suits enterprise merchants. However, full control over payments also comes with a great responsibility to protect customers’ data, and AIM carries the widest PCI DSS scope of the four methods.
Today, gateways name these options differently. Hosted gateways and server integration have become hosted payment pages, and payment links open the same kind of page. Direct Post is closest to embedded fields, though fields in the gateway’s iframe cut PCI DSS scope further. Advanced integration method is now a direct API, and plugins package one of these options for platforms such as WooCommerce. Our comparison of hosted payment pages and iframes covers the trade-offs. A merchant that adds a second or third gateway repeats one of these integrations for each provider, which is where running several gateways side by side gets harder.
Payment gateway vs payment processor
A payment gateway moves and protects the payment data at checkout. A payment processor runs the technical side, often for the acquiring bank. It carries the transaction through the card networks, then takes care of clearing and settlement. Many providers sell both together, which is why the two terms often get mixed up.
The table below adds the acquiring bank, the third party in this chain.
| Aspect compared | Payment gateway | Payment processor | Acquiring bank |
|---|---|---|---|
| Role | Moves and protects payment data at checkout | Carries the transaction through the card networks, often for the acquiring bank | Holds the merchant’s account |
| What it handles | Payment details, encryption, fraud checks, and the result shown at checkout | Approval requests and responses, clearing and settlement | Merchant risk and payouts |
| Example task | Encrypts the card details and sends the payment request | Passes the request to Visa or Mastercard and brings back the issuer’s answer | Deposits settled funds into the merchant’s account |
How a payment gateway protects card data
A payment gateway encrypts the card details, replaces the card number with a token, and screens each payment for fraud. 3D Secure is an extra check from the customer’s bank.
Encryption turns card details into code that only a system with the right key can read. The details reach the gateway over a secure TLS connection, and the gateway sends them on to the acquiring bank the same way. Tokenization protects the card number after the payment. The gateway keeps the real number in a secure vault and gives the merchant a token for refunds and repeat payments. A stolen token is useless outside the gateway.
PCI DSS is the card industry’s security standard. The PCI DSS scope is the part of the merchant’s systems that must meet it. The integration method decides how big that part is. A hosted page or the gateway’s iframe keeps it small, Direct Post widens it, and a merchant’s own payment form brings the full set of requirements.
The gateway has PCI DSS obligations of its own, covered in our article on the compliance duties a gateway provider carries.
Conclusion
The payment gateway is one of the main components of the payment process. In real time, it collects the customer’s payment details, protects them with encryption and tokenization, checks for fraud, and returns the bank’s answer to the checkout. How the gateway connects to the merchant’s site matters just as much. Each of the four integration methods puts the payment page in a different place and leaves the merchant with more or less card data to handle, which changes both the checkout and the PCI DSS scope.
PSPs, acquiring banks, and financial institutions can run this gateway layer under their own brand with Akurateco’s white-label payment gateway. It comes with 700+ integrations and is compliant with PCI DSS v4.0.1 at Level 1. Akurateco is not a payment processor and does not process transactions itself; clients bring their own acquiring.
FAQs
Is a payment gateway the same as a payment processor?
No. A payment gateway works at checkout. It accepts card details, safeguards them, and then sends the payment request on. A payment processor passes that request on to the card networks. It’s responsible for the clearing and settlement afterward. Many providers offer both services as part of a single package.
What do you need to accept payments through a payment gateway?
You need an acquiring bank or a PSP that arranges acquiring, an account with a gateway, and a way to connect the gateway to the checkout. That connection can be a hosted payment page, an iframe, a direct API, or a plugin. The site also needs a TLS certificate, and you have to meet PCI DSS for the scope your integration creates.
How long does a payment gateway take to approve a payment?
Usually a few seconds. But the gateway itself doesn’t approve the payment. The customer’s issuing bank makes that decision. The gateway collects the details, passes the request on, and shows the answer at checkout. It can take a little longer when the bank uses 3D Secure to ask the customer to confirm. The money itself reaches the merchant later, after capture and settlement.
Does a payment gateway store card data?
Many gateways do. When a merchant needs refunds or repeat payments, the gateway keeps the card number in an encrypted vault and gives the merchant a token instead. The token is useless outside the gateway, so real card numbers stay out of the merchant’s systems. The security code (CVV) is different, since PCI DSS forbids storing it after the payment is authorized.